Showing posts with label russia. Show all posts

April 01, 2022

Cybercriminals Using War to Phish Victims


Cybersecurity researchers at Google’s Threat Analysis Group (TAG) claim that government-backed hacking groups in Russia, China, North Korea, and Iran, plus various other cybercriminal groups are using the Russia-Ukraine war to phish victims and steal login credentials, sensitive information and money.

One Russian hacking group named ‘Coldriver’ or ‘Calisto’, is targeting US NGOs, think tanks, Eastern European and Balkan militaries, defence contractors, and even NATO through phishing emails sent from fresh Gmail accounts. Another example is ‘Ghostwriter’ a Belarusian group that orchestrates browser-in-the-browser attacks to spoof legitimate websites and domains to steal credentials.
Cybercriminal Hacker Fraud Theft

TAG has also warned about the ‘Curious Gorge’ hacker group which seems to be linked to the cyberwarfare branch of the Chinese military. They seem to be conducting hacking campaigns against military organisations in Kazakhstan, Mongolia, Russia, and Ukraine.

Other non-state sponsored cybercriminal groups are taking advantage of the war by impersonating military personnel and demanding payment for supposedly rescuing Ukrainian relatives. Google’s TAG has committed to continued action in identifying these malicious actors and share all relevant information to governments and industry so that we are aware of these issues and can try to protect our users as best as we can.

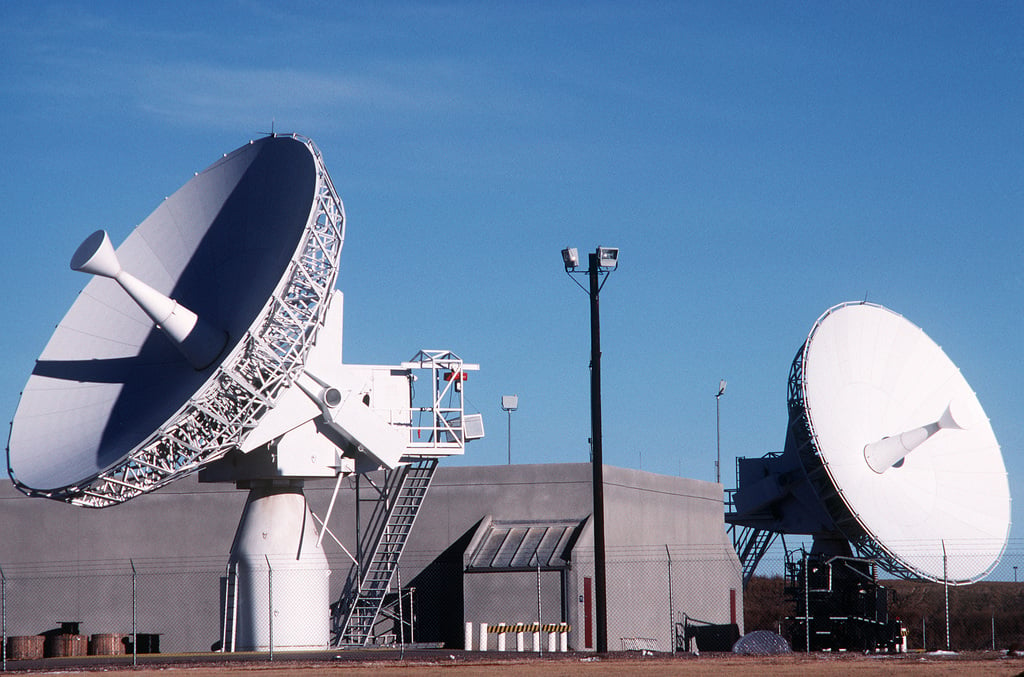
US Communications Provider Targeted by Russia


Viasat, a US satellite communications provider, recently experienced a cyberattack in February that led to service outages across central and Eastern Europe, along with disconnecting remote access to around 5,800 German wind turbines. It has now come to light that this attack was likely the result of wiper malware named “AcidRain” according to researchers at SentinelLabs. This malware was designed to erase exploitable routers and modems remotely. It wipes the filesystem and storage devices and then tries to destroy that data. After this is complete, the device is rebooted and rendered useless.

Satellite Communications System

AcidRain’s functionality is relatively simple and generic and appears to use a bruteforce attempt that signals the attackers seemed inexperienced or unfamiliar with their target or simply wanted to keep their tool reusable. The attacker’s identity is still unknown, but there are many similarities between this malware and the “VPNFilter” malware which, in 2018, the FBI attributed to a Russian-backed hacking group known as APT28. More recently, this malware was also linked to another group known as Sandworm which is notorious for its “NotPetya” malware. Both groups have been tied to Russia’s military intelligence agency, the GRU.

Viasat was able to confirm the researcher’s findings and said they were consistent with the facts provided in their own report. This report goes into more detail about the attack and explains the attackers exploited a misconfigured VPN appliance to gain remote access to the trusted management segment of their network. This allowed the attackers to execute their destructive commands remotely.

The outage has still not been fully resolved and Viasat has since shipped 30,000 modems to their affected customers. CISA have warned that US satellites may be the next target. AcidRain is potentially the seventh wiper malware to target Ukraine since the start of Russia’s invasion.